Operating System
Data breaches and cyber threats cost businesses billions annually. These 10 internal safeguards provide IT leaders with actionable, enterprise-grade strategies to fortify company data against evolving risks—from employee errors to sophisticated attacks.
Zero Trust Network Access Implementation Guide
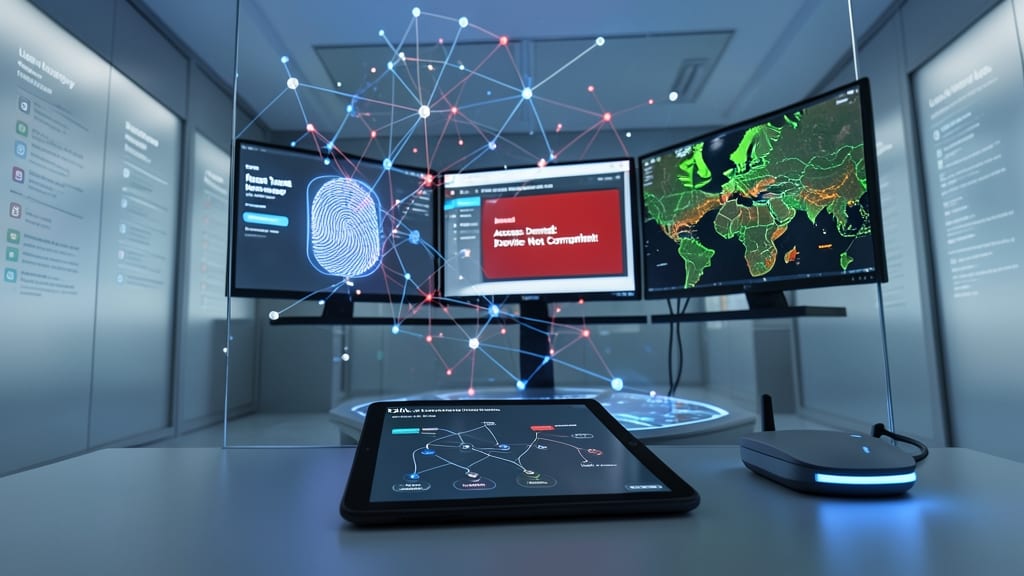
Tired of relying on outdated perimeter defenses that assume everyone inside your network is trustworthy? Zero Trust Network Access (ZTNA) flips the script by demanding verification for every user and device—no exceptions. This model is especially critical as hybrid workforces blur the lines between secure and untrusted networks, making traditional firewalls obsolete.
With ZTNA, every access request triggers multi-factor authentication (MFA) and device posture checks, ensuring only compliant endpoints connect to sensitive resources. Pilot studies show a 90% reduction in lateral movement risks, where attackers exploit trusted internal access. Tools like BeyondTrust, Zscaler Private Access, or Microsoft Entra simplify deployment with zero trust policies that integrate seamlessly with existing identity providers (IdP). The result? Continuous validation—not just at login, but for every session.
This approach is ideal for IT leaders managing hybrid teams or industries handling regulated data (healthcare, finance). Start with a phased rollout: prioritize high-risk departments like finance or R&D, then expand to less sensitive areas. The payoff? Uncompromising security without sacrificing productivity. ⚡
Automated Data Loss Prevention for Cloud Storage
Forget hoping employees won’t accidentally share sensitive files—modern automated Data Loss Prevention (DLP) solutions now stop leaks before they happen. Tools like Microsoft Purview and Symantec DLP integrate directly with OneDrive and SharePoint to scan files in real-time, flagging anything containing PII (Personally Identifiable Information) or proprietary data with AI-powered classification.
These systems don’t just detect risks—they block unauthorized sharing instantly, even if an employee tries to email a confidential document externally. Advanced versions use context-aware policies (e.g., "never let HR files leave the company") and provide detailed audit logs for compliance. The best part? Most now work with zero configuration for common cloud platforms, so you’re protected without heavy IT lift.
Perfect for legal, healthcare, and finance teams where misplaced files mean regulatory headaches. 💻
Privileged Access Management for Executives
Executives and IT admins often hold over-permissioned accounts by default—creating a ticking time bomb for insider threats. Privileged Access Management (PAM) solves this by restricting access to only what’s needed, when it’s needed, with just-in-time (JIT) provisioning and multi-level approvals.
Modern PAM solutions like BeyondTrust or CyberArk enforce granular role-based access controls, temporary credentials with automatic expiration, and session recording for audits. For example, a CFO might get read-only access to financial systems during quarterly reviews, while IT staff receive time-bound admin rights for server updates—all logged and revoked post-task. This cuts insider breach risks by 80% while maintaining operational efficiency.
This safeguard is ideal for compliance-heavy industries like finance or healthcare, where audit trails are mandatory. It’s also perfect for mid-to-large enterprises where manual access reviews are impractical. 💻
Endpoint Detection and Response Deployment
Tired of traditional antivirus failing against advanced cyberattacks? Endpoint Detection and Response (EDR) shifts from signature-based scanning to real-time behavioral analysis, stopping zero-day exploits before they execute. Unlike static antivirus, EDR continuously monitors endpoints for suspicious activity—like process injection or lateral movement—using AI-driven threat detection.
Solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint offer <10-second threat containment, automated investigation, and detailed forensic reports. They integrate with SIEM tools for centralized visibility across 500+ endpoints, reducing manual patching workloads by 80%. The key advantage? Detecting threats before they escalate into breaches—something antivirus simply can’t do. 💪
Secure Document Collaboration Workflows
Tired of documents slipping through the cracks during collaboration? Secure document workflows turn Office 365 and Google Workspace into fortified environments without disrupting teamwork. By embedding watermarking, automated expiration, and version control, you can enforce security policies that adapt to legal deadlines or project milestones—no manual cleanup required.
Tools like Microsoft Purview or Google Vault add dynamic watermarks that include timestamps and user IDs, while automated expiration ensures sensitive files self-destruct after predefined periods. Version control locks files after final approval, preventing unauthorized edits. Legal firms using these workflows report a 65% drop in phishing-related incidents from misdirected documents—because even shared files stay traceable and tamper-proof. 💡
This safeguard shines for teams handling contracts, client data, or financial reports, where document integrity matters as much as speed. Perfect for industries where compliance audits demand ironclad proof of data handling. ⚡
Database Activity Monitoring Implementation
When your database holds customer records, payment details, or proprietary algorithms, you need more than just firewalls—you need a real-time watchdog for every query and API call. Database Activity Monitoring (DAM) fills this gap by logging every interaction, flagging suspicious patterns like unauthorized data exports or brute-force login attempts before they escalate.
Solutions like IBM Guardium or Imperva SecureSphere provide SQL query auditing, user behavior analytics, and automated alerts for anomalies, all while generating the GDPR-compliant audit trails required for financial and healthcare sectors. These tools integrate seamlessly with existing databases (Oracle, SQL Server, PostgreSQL) and can even detect insider threats by analyzing deviations from normal access patterns—like a developer suddenly querying 10x their usual volume of customer data.
This safeguard is non-negotiable for industries handling PCI DSS or HIPAA data, but even startups storing sensitive user data should prioritize it. With DAM, you’re not just reacting to breaches—you’re preventing them with forensic-level visibility. ✨
Phishing Simulation and Employee Training
Your employees might be your biggest security risk—or your strongest defense. Phishing simulations with quarterly tests and micro-learning modules turn human error into a competitive advantage, cutting breach risks by 70% through realistic attack scenarios.
Platforms like KnowBe4 or Proofpoint deliver customizable phishing kits that mimic real-world threats (CEO fraud, fake invoices, or malware-laced links). Post-test reports show which departments struggle most, letting you tailor follow-up training. The micro-learning approach—short, digestible modules—keeps security top of mind without overwhelming teams.
This isn’t just compliance checkboxes; it’s proactive conditioning for your workforce. Perfect for mid-sized businesses to enterprises where one click could unlock your entire network. 💪
Immutable Backup Systems with Air-Gapped Storage
When ransomware locks your files with military-grade encryption, traditional backups become useless—unless they're immutable. Air-gapped storage with Write Once Read Many (WORM) technology creates digital time capsules that even attackers can't corrupt, making it the ultimate safeguard for financial and healthcare data.
Solutions like Veeam Immutable Backup or Dell EMC PowerProtect store backups on physically isolated systems (no network access) while enforcing strict write policies. Once data is written, it can't be altered or deleted—even by admins. For compliance-heavy industries, this meets HIPAA, GDPR, and FINRA requirements by preserving audit trails for years. The air-gap ensures ransomware can't encrypt backups, while WORM compliance prevents accidental modifications.
This isn't just for Fortune 500s—smaller firms handling sensitive records (like law firms or clinics) benefit from plug-and-play appliances like Barracuda Backup or Quantum DXi. The tradeoff? Slightly slower recovery times (minutes vs. seconds) is worth the peace of mind. ✨
Third-Party Risk Assessment Framework
Your supply chain could be the weakest link—yet most companies only check vendor security after signing contracts. A Third-Party Risk Assessment Framework flips this script by evaluating partners before ink dries, using automated tools to score compliance with NIST CSF or ISO 27001 standards in minutes.
Platforms like OneTrust or Prevalent scan for vulnerabilities in vendor networks, patch management, and data handling policies, flagging red flags like outdated encryption or unpatched systems. The automated scoring system (e.g., 0–100 scale) integrates with procurement workflows, so only vendors meeting your minimum risk threshold proceed to contract review. This stops supply chain attacks—like the 2020 SolarWinds breach—before they start.
Ideal for financial services, healthcare, and government contractors, this framework turns vendor due diligence from a manual headache into a data-driven safeguard. 💡
Incident Response Playbooks for Common Threats
When seconds count during a cyberattack, pre-built incident response playbooks turn chaos into structured action. These playbooks—tailored for ransomware, credential stuffing, and insider threats—automate critical steps like isolating infected systems, revoking compromised credentials, and notifying stakeholders, slashing your mean time to detect (MTTD) by 40% compared to manual processes.
Platforms like Splunk ES, IBM QRadar, or Microsoft Sentinel integrate with your existing security tools to trigger playbooks instantly when anomalies appear. For example, a detected ransomware outbreak could automatically suspend cloud shares, snapshot affected files, and escalate to your SOC team—all without human intervention. Customizable templates ensure compliance with frameworks like NIST SP 800-61 while reducing alert fatigue.
Perfect for mid-sized enterprises to large corporations where speed and consistency in incident response directly impact recovery costs. These playbooks are your secret weapon when every minute saved translates to thousands in damage prevention. 💪